A plain QR code cannot prove that a product is genuine, because anyone can photograph the symbol and print it on a fake. QR-based authentication only means something when the code is one part of a wider system: a unique identifier per item, a trusted verification service, duplicate-scan analysis, signed data or a physical security feature.
The QR symbol is still a good phone-readable bridge between an object and that system. This guide explains why a basic label fails, the main architectures and what each one stops, where to place codes on a pack, how to word the result a shopper sees, and the checks to make before you trust a "genuine" message. For shelf stickers and fake overlays in stores, see the retail guide.
Why is a plain QR code easy to copy?
A standard QR code is built to be readable, not secret. Anyone who can photograph or scan it can reproduce the same modules on another label.
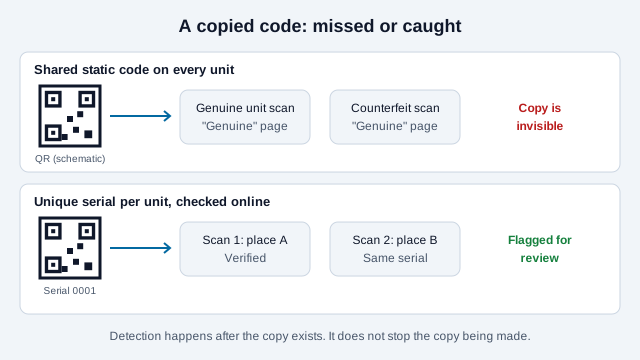
If one shared code opens a page saying "This product is authentic", a counterfeiter can copy the code and often imitate the page. The scan proves only that the printed pattern contains a particular URL. It does not prove that the label belongs to the object in your hand. A vendor article from a QR generator company makes the same point: a static code on every unit has no authentication value, and a batch-level code is weak because one copy validates every fake in the run.
A public information code is still useful for manuals, ingredients and support. Do not market it as anti-counterfeit unless the system behind it tests authenticity. The scale of the problem is real: the OECD and EUIPO estimated global trade in counterfeit goods at about USD 467 billion in 2021 in their 2025 report, which is why brands look for scannable checks.
How does serialized QR authentication work?
Serialization gives every item its own identifier instead of printing the same code on every unit. A verification service stores the issued identifier, the product record, its status and relevant supply-chain events. Identifying an item is not the same as verifying it; the GS1 Digital Link guide shows how the identifier itself is structured.
- The brand creates a unique identifier for each item.
- A controlled system generates the code and the matching record.
- The code is printed or applied during production.
- A shopper, distributor or inspector scans the item.
- The service checks whether the identifier exists and what its history says.
- The page returns an understandable result and a safe next step.
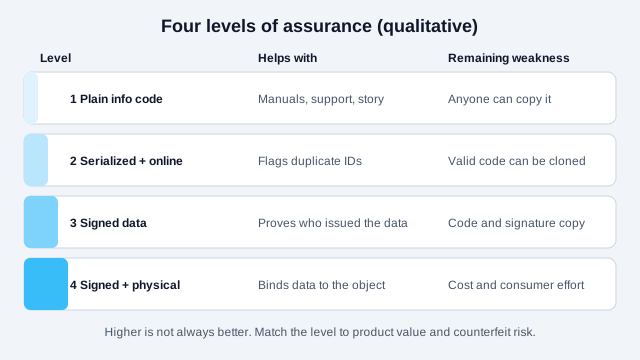
Serialization raises the cost of broad copying and enables anomaly detection, but a valid code can still be cloned. The system has to interpret repeated observations, not declare every known identifier genuine forever.
What can duplicate-scan analysis detect?
Scan analysis flags patterns that are implausible or inconsistent with the product's expected market. GS1's digital-signature guidance describes mass serialization and conflicting observations as ways to detect cloned instances. Common signals:
- the same serial scanned in distant places within an impossible time;
- far more first-time scans than one unit could produce;
- scans before the recorded manufacture or release;
- an identifier appearing in a market where it was never shipped;
- a revoked, returned or destroyed item scanned again.
The limits matter. Detection identifies suspected copies after they exist and does not prevent them, and a monitoring dashboard nobody reads catches nothing. Scans can also come from innocent causes: a gift scanned by two relatives, a retailer checking stock, a reseller scanning twice. Location data can be incomplete, shared or privacy-sensitive. Treat the signals as leads for a human to investigate, not proof that a particular buyer holds a fake.
What do digital signatures add?
A digital signature lets a verifier confirm that the encoded data came from an accountable signer and was not altered. GS1 publishes a digital-signature standard for this, built on established technology and independent verification. The verifier checks the signature using the issuer's public key. If the signed identifier or attributes change, verification fails, which is stronger than a web page that merely looks official.
A signature does not bind the data to the object. A signed payload and its QR symbol can be copied together onto another item, and a copied code that is already valid will verify again. GS1's guideline relies on serialized identifiers so that a cloned instance can be spotted when it appears in two places at once. Brands often add physical security elements such as watermarks, holograms, microprinting or special inks on top; that layering is common practice here, not something this guide found GS1 prescribing.
Which physical features strengthen the system?
A second physical element makes it harder to move a valid digital identity onto a counterfeit object. It can be visible, hidden, destructible or readable only with special equipment.
| Feature | What it adds | Trade-off |
|---|---|---|
| Tamper-evident label or seal | Breaks if removed, so a peeled and reapplied code is visible | Shoppers must notice it |
| Hologram or optically variable element | Hard to reproduce cheaply | Needs a viewer who knows the genuine look |
| Microprinting, UV or special inks | Covert check for inspectors | Needs equipment |
| Code hidden inside sealed pack | Cannot be photographed from the shelf | Verification happens only after opening |
| Copy detection pattern in the print (vendor technology) | A printed graphic that degrades when copied, so a scan can tell original from copy | Vendor-reported; needs controlled print quality |
| NFC or secure hardware | Stronger item-level binding | Higher unit cost, for high-value goods |
The right mix depends on product value, counterfeit incentive, inspection channels and cost. A consumer check and an inspector-only forensic check can serve different assurance levels. No independent evaluation of how well these schemes resist cloning was found while preparing this guide, so treat vendor claims as claims.
Where should the codes sit on the pack?
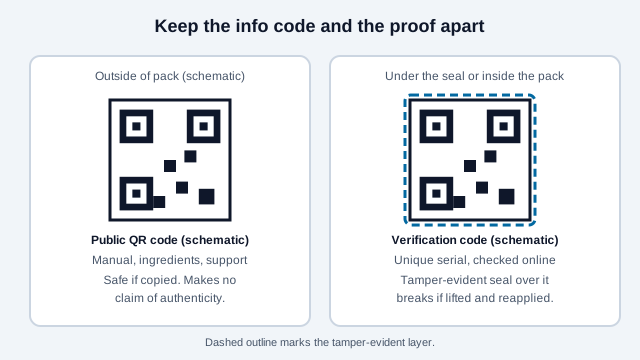
Keep the code that anyone may scan apart from the one that proves anything. An outside code can open the manual and make no claim of authenticity. A verification code under a tamper-evident seal, or inside the pack, is harder to harvest from a shelf photo. A sticker that can be peeled and reapplied is not an authentication control, and a fake sticker placed over a real code is a separate danger covered in the QR scam guide.
How should the verification result be designed?
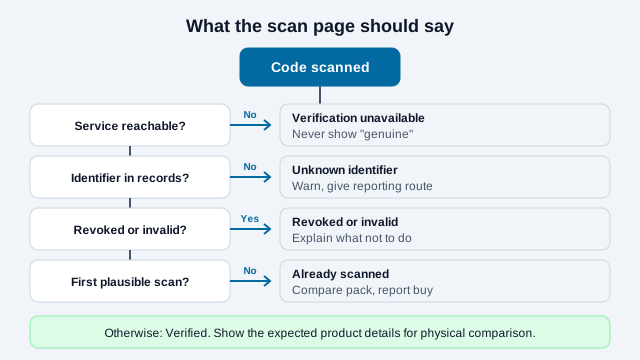
Communicate uncertainty honestly. A universal green "genuine" message teaches counterfeiters exactly what to imitate.
| Result | Meaning | Suggested action |
|---|---|---|
| Verified | Checks passed and no risk rule fired | Show expected product details for comparison |
| Already scanned or unusual | The identifier may be copied or the context is unexpected | Ask the user to compare the pack and report purchase details |
| Unknown identifier | The code is not in the trusted issuance record | Warn and give an official reporting channel |
| Revoked or invalid | The item should not be accepted | Explain what not to do and how to contact the brand |
| Verification unavailable | The service could not complete the check | Never silently say genuine; offer a later path |
What do regulated sectors do instead?
Some sectors have their own rules, and a consumer QR code may not be the permitted carrier. In the EU, medicines carry a unique identifier in a 2D Data Matrix code plus an anti-tampering device under Delegated Regulation (EU) 2016/161, applied from 9 February 2019, and pharmacies verify and decommission the identifier when they dispense. Rules differ outside the EU. GS1 states that GS1 DataMatrix, not QR Code, is used for product identification and traceability in its healthcare framework. Food, alcohol, cosmetics, electronics and digital product passport programs can also carry separate labeling, privacy and recordkeeping duties. See the healthcare QR guide and the Digital Product Passport guide.
Rollout checklist: how do you roll out an authentication code?
- Name who counterfeits what, where verification happens and what decision follows.
- Pick the carrier and data standards your sector uses.
- Define unique identifiers, issuance controls, activation, revocation and retention.
- Choose online record, signature, physical feature or a combination.
- Protect generation credentials, signing keys, production files and admin accounts.
- Write duplicate and impossible-travel rules, with a human investigation process.
- Design clear shopper results and an official reporting channel.
- Test copying, photographing, label transfer, page imitation, outages and privacy behavior.
- Proof the print with the scannability tester and plan hosting for the product lifetime (see why QR codes stop working).
- Monitor continuously and publish a retirement or migration plan.
What mistakes weaken an authentication program?
Picture a small supplement brand that prints one QR code on every bottle linking to a page with a green tick and the word "Authentic". Six months later a knock-off appears with the same code, the same page copy and a slightly different cap. Every scan of the fake shows the tick, and the brand's own dashboard shows nothing unusual because it counts scans, not serials. The usual mistakes:
- Calling a shared information code "anti-counterfeit".
- Using batch-level codes and expecting item-level proof.
- Returning "genuine" when the server is unreachable.
- Leaving the verification code exposed on the outside of the pack.
- Collecting scan locations with no privacy notice or retention limit.
- Printing codes before a revocation and reporting process exists.
What this guide cannot settle
No checklist settles the threat model for your category, which security feature is cost-effective at your volume, or how many shoppers will actually scan. Duplicate-scan thresholds need tuning with real data, and independent evidence on cloning resistance is thin, so most published claims come from vendors. Standards such as ISO 22383 give guidelines for evaluating authentication solutions, but a standard does not choose the design for you.
This article is an editorial overview, not legal or security advice. Medical products, food, alcohol, cosmetics and electronics have sector rules, so obtain standards and legal guidance before treating a QR implementation as compliant. For simple, non-security uses, a static code is free and never expires.
References
- GS1: GS1 Digital Signatures standard
- GS1: Digital Signatures Technical Implementation Guideline
- GS1: 2D barcode in healthcare
- GS1: QR code security measures and potential misuse
- OECD: Global trade in fake goods reached USD 467 billion (press release, 2025)
- QRStuff: How to use QR codes for product authentication (vendor article)
- Scantrust: Why secure QR codes are the future of anti-counterfeiting (vendor article)
- MHRA Inspectorate: Falsified Medicines Directive safety features